PROBLEM
Your AI use is creating risk before it creates value.

While your business:
Uses AI tools without a clear policy
Staff may paste sensitive data into public tools
Has no approved AI use-case register
Has no clear owner for AI risk or compliance
Has no audit trail for prompts, outputs, and decisions
Responsible firms have:
Clear AI usage rules for every team
Approved tools, workflows, and data boundaries
Governance aligned to risk, compliance, and operations
Practical oversight that supports innovation without slowing teams down
HOW IT WORKS
The 3-Phase AI Governance Framework
Our AI governance review maps how AI is being used, where risk sits, and what controls are needed to use AI safely.


01
STEP (1-3 Days)
Discover and Assess
We assess current AI usage, tools, data handling, decision points, and governance gaps. You get a ranked risk and opportunity register.
02
STEP (4-14 Days)
Build the Governance Framework
Policy, approved use cases, staff guidance, data controls, review processes, and escalation routes — all tailored to your business.

03
STEP (48–72 Hours):
Monitor and Improve
We help track adoption, incidents, policy gaps, and control effectiveness so your AI governance keeps pace with usage.
About the Founder
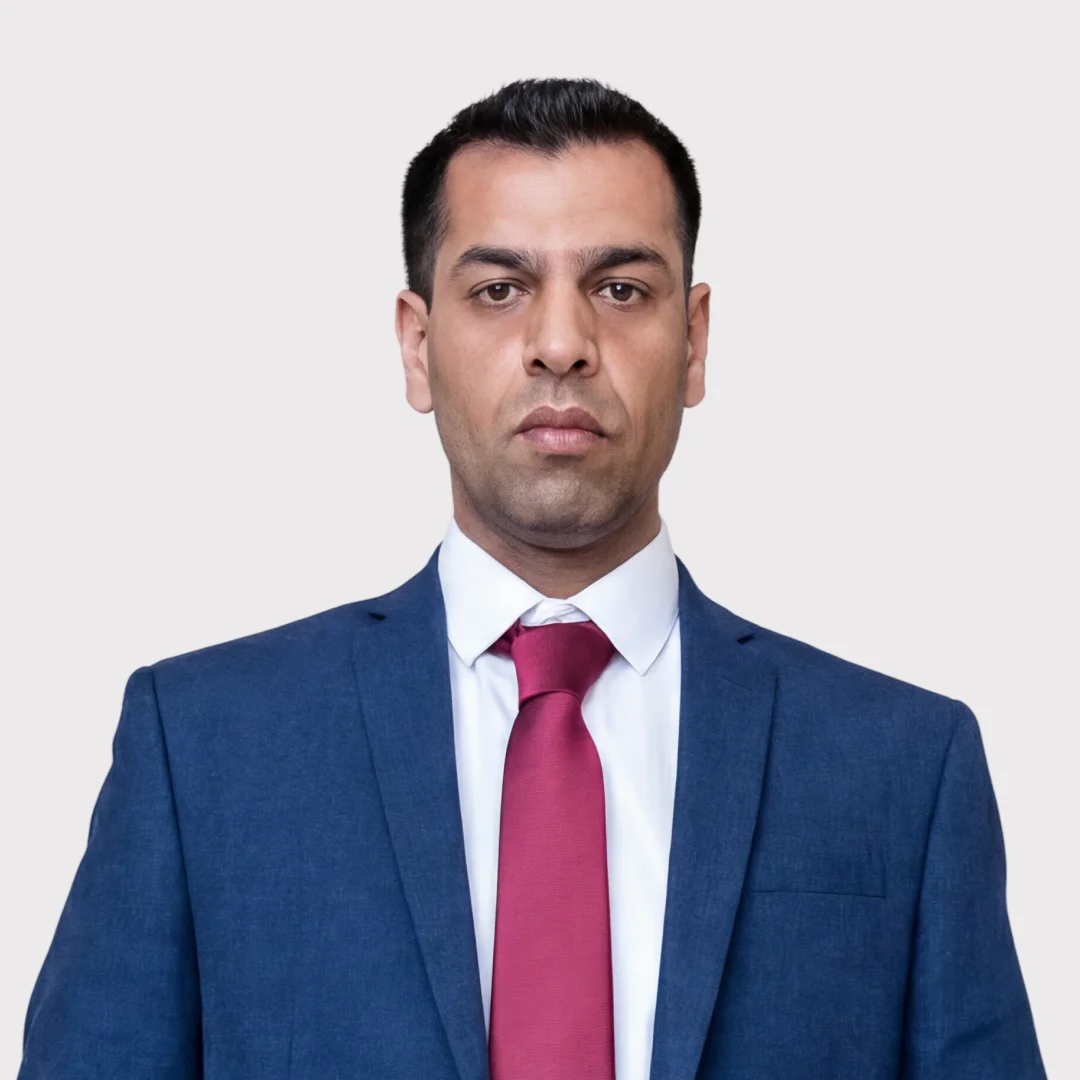
Mohammed Yaqoob
Mohammed Yaqoob has over 14 years’ experience inside major financial institutions in the City of London and Canary Wharf.
His background spans the aftermath of the Global Financial Crisis helping banks and broker-dealers rebuild their standing amongst clients, regulators and investors, re-engineering their prudential risk frameworks and governance.

Over time, he noticed the opportunity.... Financial firms had gone through rigorous discipline and transformation to identify and assess risk better in the face of one of the greatest challenges to the global economy.
How can that be harnessed for the next great challenge of AI? AI Whisperer was born to help seize those opportunities.
Today, Mohammed applies the same compliance-aware, systems-driven thinking to AI-powered client growth, helping financial services firms build scalable solutions that generate consistent, qualified conversations.
Because in finance, structure matters. And growth should be engineered, not left to chance.
FAQ
AI GOVERNANCE
Safer AI adoption
Give teams the confidence to use AI without exposing sensitive data, creating shadow processes, or increasing compliance risk.
Clear usage boundaries
Define which tools, tasks, data types, and workflows are approved so staff know what is safe and what needs review.
Better data protection
Clarify how confidential information, client data, and internal documents should be handled when AI tools are used.
Policy clarity
Turn vague AI concerns into practical rules that are easy for staff to understand, follow, and apply.
Oversight you can trust
Create a governance trail around use cases, risks, approvals, responsibilities, and review points.
Audit-ready workflows
Document how AI is used across the business so you can demonstrate control when clients, regulators, or internal stakeholders ask.
HOW IT COMES TOGETHER
01
We review how staff use AI today, what tools are involved, what data is being entered, and where controls are missing.
02
We turn governance into clear rules, approved uses, data boundaries, escalation routes, and ownership.
03
Responsibilities, review points, and decision controls are defined so AI use is not left to individual judgement alone.
04
Reporting focuses on adoption, policy gaps, incidents, data handling, and the next controls needed as AI usage matures.
Get started today
Start with a clear AI usage checklist.
See where AI is already being used, what risks matter most, and which controls should come first.